cd /news/ai-crawlers/structured-forms-for-private-vulnera… · home › topics › ai-crawlers › article
[ARTICLE · art-143492] src=github.blog ↗ pub= topic=ai-crawlers verified=true sentiment=↑ positive

Structured forms for private vulnerability reports

GitHub now requires reporters filing private vulnerability reports to complete a structured form with four required fields — summary, details, a proof of concept of at least 150 characters, and impact — replacing the single free-text box that made low-quality or AI-generated reports easy to submit. Maintainers can customize the form via a .github/VULNERABILITY_REPORT.yml file on the default branch, require a CWE assignment through Settings > Advanced Security > Private vulnerability reporting, and reporters can check "I used AI assistance to find or write up this report" to disclose AI use. The feature is available for public repositories with private vulnerability reporting enabled on GitHub Free, GitHub Pro, GitHub Team, and GitHub Enterprise Cloud, and custom forms must be matched by REST API submissions, with mismatches returning an error pointing to a new endpoint that returns the enforced form.

by read2 min views2 publishedOct 1, 2026
Structured forms for private vulnerability reports
Image: GitHub Changelog

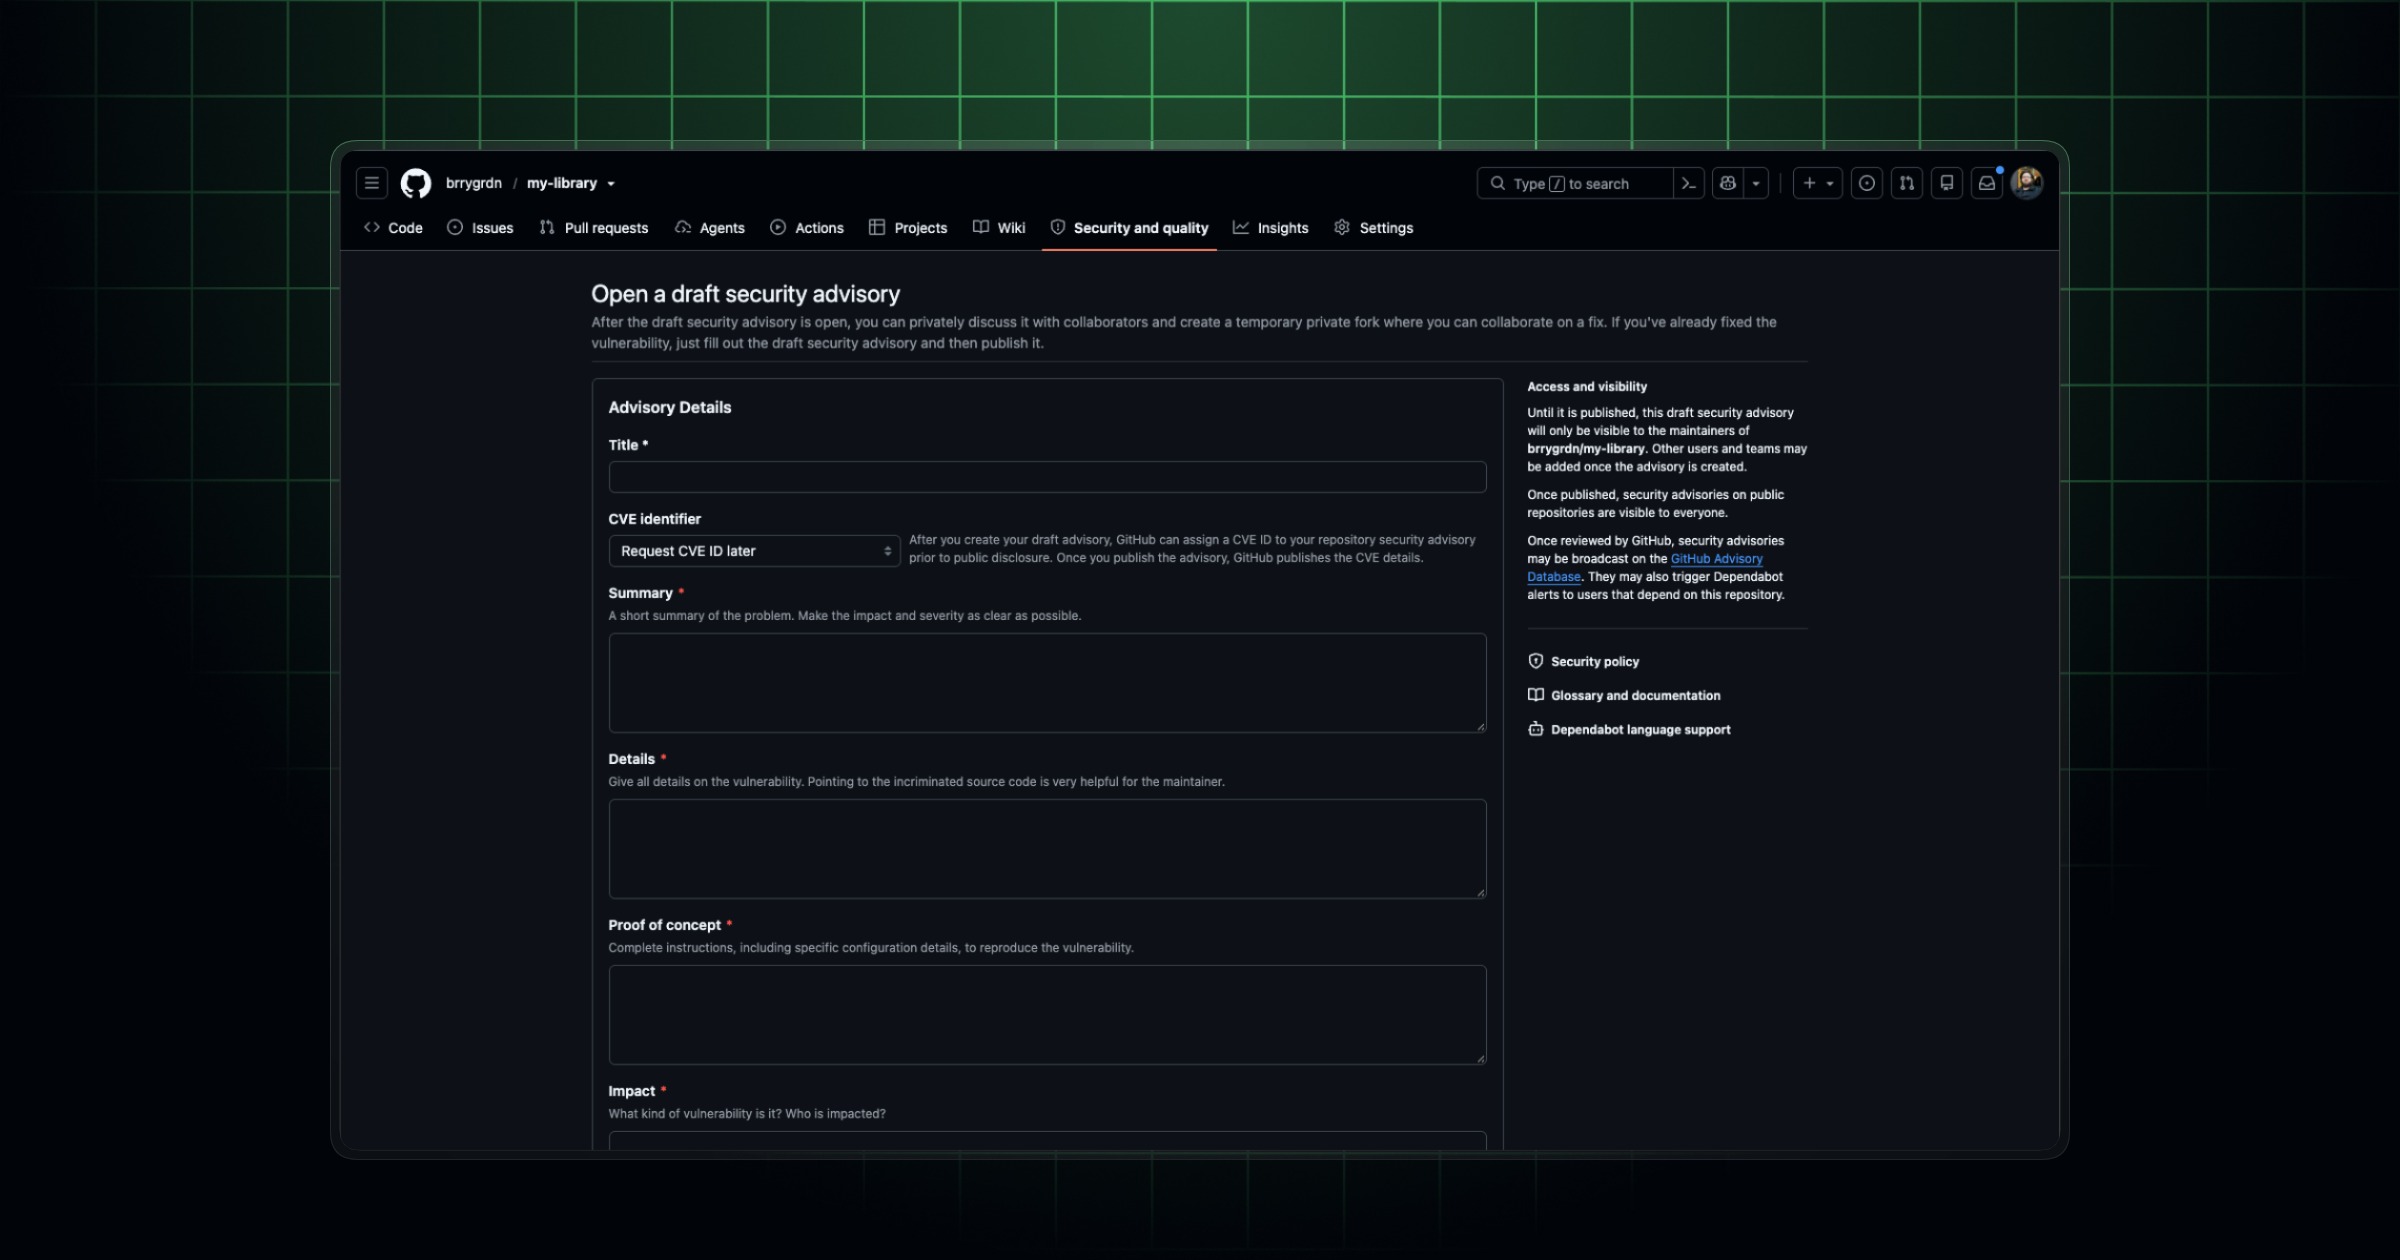
Private vulnerability reports can now use a structured form that asks reporters for the details you need to assess a vulnerability, including a reproducible proof of concept. A single free-text box made it easy to submit low-quality or AI-generated reports and hard for you to find the signal in them. Now, by default, reporters must fill in four required fields: summary, details, proof of concept (at least 150 characters), and impact. Their answers are combined into the advisory description, so you review and edit the report as you do today.

With this update:

  • You can customize the form by adding a .github/VULNERABILITY_REPORT.yml file to your repository’s default branch. To apply a form to all repositories you own, add it to your organization or account’s.github repository. Forms use issue form syntax, and fields supportmin_length so you can require a minimum level of detail. If your form is invalid, the default form is used.
  • You can require reporters to assign a CWE before they submit, from Settings >Advanced Security >Private vulnerability reporting . Organization and enterprise owners can enforce this setting through a policy.
  • If your repository has a security policy, reporters see a banner linking to your SECURITY.md before they submit.
  • Reporters can check “I used AI assistance to find or write up this report” to disclose AI use.

If you add a custom form, reports submitted through the REST API must match it. The default form isn’t enforced for the API, so existing integrations keep working. When an API submission doesn’t match, the error points to a new endpoint that returns the form your repository enforces. This is available for public repositories with private vulnerability reporting enabled on GitHub Free, GitHub Pro, GitHub Team, and GitHub Enterprise Cloud.

Learn more about privately reporting a security vulnerability.

── more in #ai-crawlers 4 stories · sorted by recency
── more on @github 3 stories trending now
sponsored brought to you by zahid.host 4,200+ EU-deployed projects
reading about agents? ship yours in a single git push.

Run your AI side-project on zahid.host

EU-based hosting, git-push deploys, automatic HTTPS, no cold starts. Free tier with a custom domain — perfect for shipping the agent you just read about.

$git push zahid main
→ Live at https://your-agent.zahid.host ✓
Get free account → Pricing
from €0/mo · no card required
LIVE [news/structured-forms-for…] indexed:0 read:2min 2026-10-01 · —