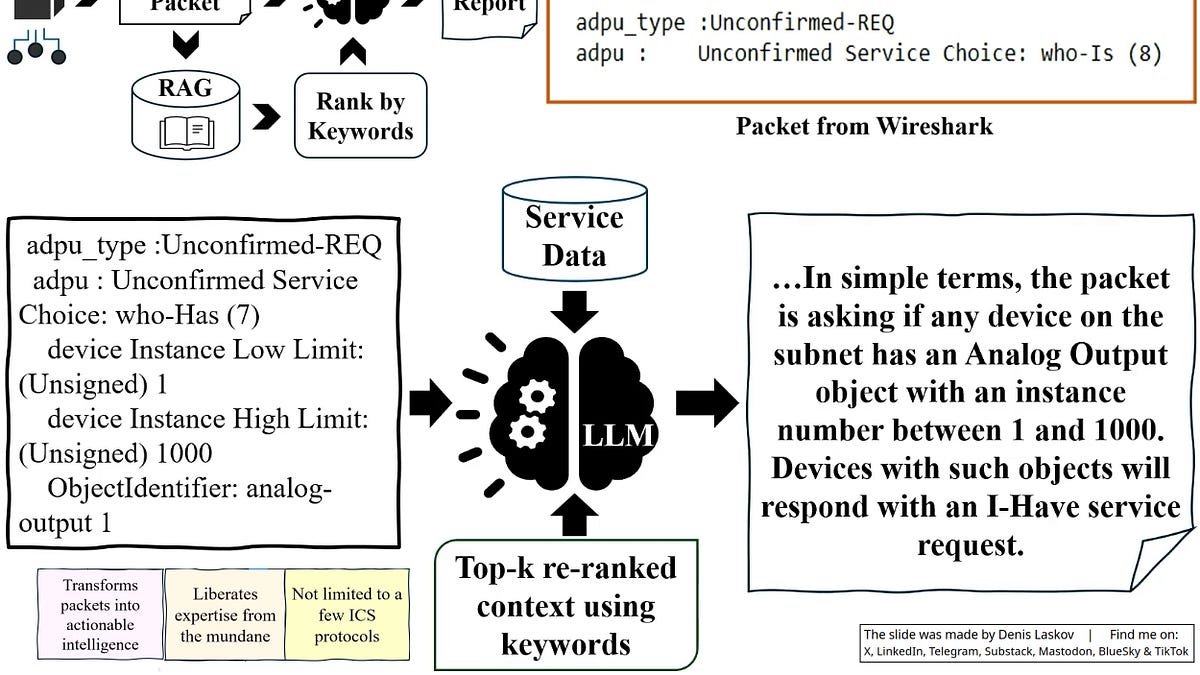
A group of security researchers from Japan and Singapore shared their approach to getting extra context and information for SOC team members for security attribution of packets in OT protocols: of course, using LLMs.
The idea is simple - some OT protocols have enough documentation and data online, but you cannot expect every SOC member to know them. However, during incident response, this knowledge becomes vital. To add this knowledge, the Panasonic team proposes using LLM processing pipeline, where the model adds context to the packet.
Great minds think alike, and we also use this approach for some of our tasks. This enriches the analysis with a lot of context that is currently lacking in off-the-shelf systems for OT and critical infrastructure.
Interesting work, and I’m glad that someone else is trying to solve OT security problems by adding knowledge.
More details:
AI Analysis of OT Packets For SOC Analysts [Youtube]: https://lnkd.in/dSUtmHbf PAIEL: Protocol-Aware and Context-Integrated Protocol Explanation Using LLMs for SOCs [PDF]: https://www.ndss-symposium.org/wp-content/uploads/wosoc26-13.pdf