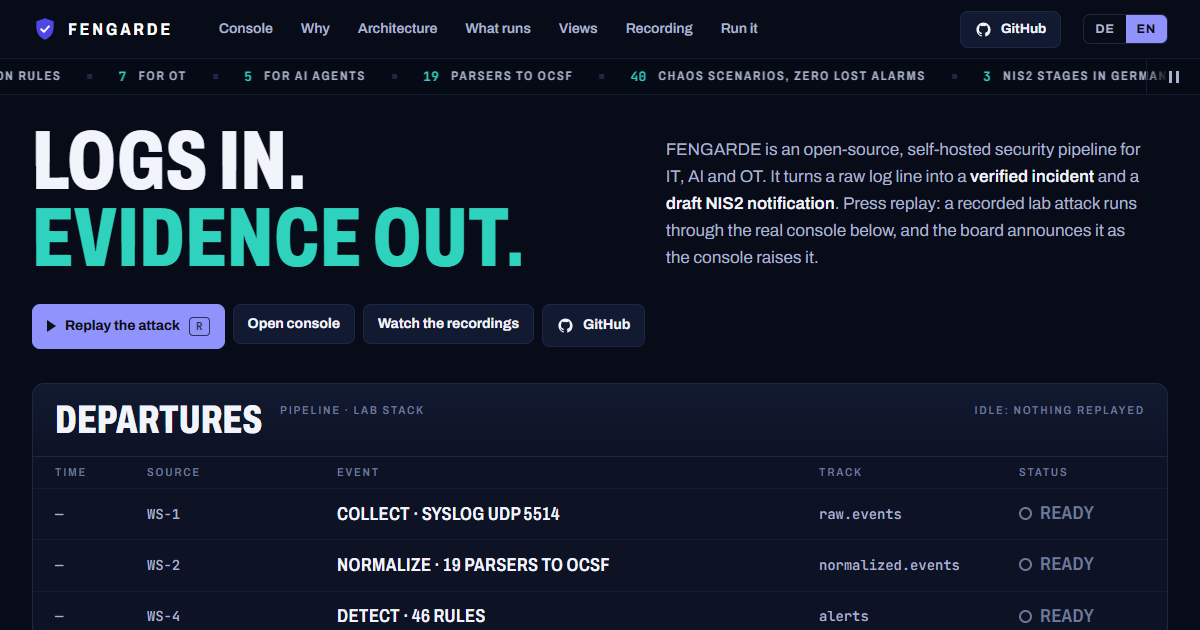
Evidence out.
FENGARDE turns a raw log line into a verified incident and a draft NIS2 notification.
Departures #
pipeline · lab stack Idle: nothing replayed
| Departure board: pipeline stages and the alarms raised by the replayed attack | ||||
|---|---|---|---|---|
| Time | Source | Event | Track | Status |
| --- | --- | --- | --- | --- |
Track= bus topic.
One pipeline. Receipts included. #
Seven things FENGARDE does that a log viewer does not. Each names the place in the repository where you can check it.
Nine services. One bus. #
No service calls another. Each reads topics from the bus and writes topics back, so any stage can be restarted, swapped or scaled alone. Every box opens its directory on GitHub, and during a replay the boxes light as the attack passes through them.
Swipe sideways to see the whole bus.
What runs. What does not. #
Every capability gets the board's honest word. Anything stubbed, opt-in or not built says so.
| Capability board | |||
|---|---|---|---|
| Service | What | Interface | Status |
| --- | --- | --- | --- |
46 rules, all listed. #
Read straight from the rule files in the repository: level, title and the MITRE ATT&CK (or ATLAS, or ICS) tag each one carries.
Twelve views. Open any. #
Each tile opens that view of the real console on the recorded data.
One take, no cuts. #
Recorded in a scripted browser against a running stack. A real SSH brute force and a DNS burst go in over UDP 5514 at about 0:30.
Run it in ten minutes. #
$ git clone https://github.com/supermhel/fengarde.git
$ cd fengarde && make preflight
$ make demo          # an SSH brute force becomes a real alarm

$ cd tools/console_e2e && npm install
$ node check.mjs       # every view as admin, analyst, read-only
$ node tour.mjs out    # re-records the video, sends the attack
- Docker Desktop with enough memory for OpenSearch. make preflight checks ports and limits before the first start.
- The console, its checks and this page's video all come from the repository:
services/ws7-dashboard/app,tools/console_e2e. - The UDP syslog listener is unauthenticated: expose port 5514 on a trusted network or VPN only.
- Status, proven versus claimed: SSOT.md . Features per view:console feature matrix .