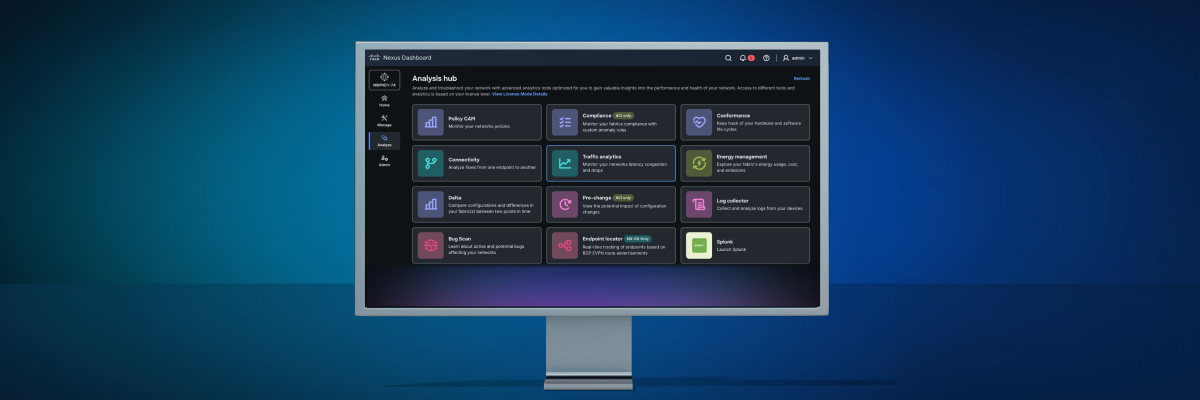
In today’s fast-evolving data center environments, scaling and managing complex and distributed networks for traditional and AI workloads demand immediate, actionable insights. Teams need real-time visibility to resolve issues faster, turning raw, high-volume network data into fast, confident decisions. Cisco addresses this challenge with the native Splunk integration within Cisco Nexus One, a transformative embedded analytics solution designed to accelerate troubleshooting, ensure data sovereignty, and optimize operational costs by correlating workflows for NetOps, ITOps and SecOps (Figure 1).
What is native Splunk in Cisco Nexus Dashboard? #
Native Splunk within Cisco Nexus Dashboard, providing on-premises management as part of the Cisco Nexus One architecture, delivers robust, scalable, production-ready observability. Unlike traditional approaches that send telemetry data to external clouds or centralized platforms, native Splunk processes high-fidelity telemetry—such as anomalies, advisories, and audit logs—for analysis locally on Cisco Nexus Dashboard. This on-premises deployment eliminates latency and reduces time and costs associated with data egress, while providing a unified management and analytics experience.
Here is a demonstration of how it works.
Key benefits and value of native Splunk on Cisco Nexus Dashboard #
- Unified visibility : Federated dashboards deliver cross-domain (e.g., campus, WAN and data center) insights across network, security, and configuration events regardless of data origin, simplifying operational workflows.
- Accelerated root cause analysis (RCA) : By correlating configuration changes, network anomalies, and audit logs in real time on a single dashboard, native Splunk drastically reduces mean time to resolution (MTTR). This enables network and security teams to identify issues in minutes rather than hours.
- Embedded analytics : Users can access instant dashboards, custom searches, and alerts directly within Nexus Dashboard’s Analysis Hub, without requiring separate Splunk deployments.
- Data sovereignty and compliance : Processing telemetry locally ensures sensitive data remains on-premises, supporting regulatory compliance and data residency requirements.
- Operational cost efficiency : Local analytics reduce cloud storage and data transfer costs by minimizing the need to send large volumes of raw telemetry data offsite.
Key native Splunk features and use cases #
Native Splunk uses Splunk Operator for Kubernetes and runs as a microservices-based architecture, providing flexibility and scalability. The following are key use cases and features provided by native Splunk.
Real-time root cause analysis
Native Splunk ingests high-fidelity telemetry data such as anomalies, advisories, and audit logs directly from Nexus Dashboard through Splunk’s HTTP Event Collector (HEC). This telemetry includes system and fabric events streamed in real time. By correlating configuration changes (e.g., audit logs) with network anomalies (e.g., packet drops, congestion) on a unified Splunk dashboard embedded within Nexus Dashboard, network and security teams can pinpoint RCA rapidly. The local processing eliminates latency and avoids the need to ship large volumes of raw data to external platforms, enabling MTTR reduction from hours to minutes.
End-to-end network visibility Native Splunk provides federated dashboards that unify cross-domain insights across network, security, and configuration events. It collects telemetry from multiple Cisco data center components, such as NX-OS switches, ACI fabrics, and Nexus Dashboard itself. Data ingestion is achieved through syslog, Representational State Transfer (REST) APIs, and event streaming configured within the Nexus Dashboard environment. This unified visibility allows monitoring of network health, security advisories, and configuration compliance from a single platform, simplifying operational workflows.
Cost optimization
By embedding Splunk natively on Nexus Dashboard nodes (ND-NODE-G5S and ND-NODE-G5L), telemetry data is processed locally with a daily ingestion limit of 10 GB and 30-day retention. This on-premises analytics approach reduces cloud storage and data egress costs by minimizing the transfer of telemetry data offsite. The embedded Splunk instance automatically streams only relevant telemetry categories (e.g., anomalies, advisories, audit logs) from Nexus Dashboard, avoiding unnecessary data duplication.
Regulatory compliance
Processing telemetry locally within Nexus Dashboard ensures sensitive operational data remains on-premises, supporting data sovereignty and regulatory compliance requirements. The embedded Splunk instance synchronizes user and role management with Nexus Dashboard, maintaining secure access controls. Audit logs and advisories are streamed directly to the local Splunk instance, preventing exposure of sensitive data to external cloud environments.
Unified operations and automation
Native Splunk integrates with Nexus Dashboard’s Analysis Hub, enabling users to launch Splunk dashboards and perform custom searches without separate Splunk deployments. The platform supports AI/ML-driven insights and automation workflows in AgenticOps that can trigger playbooks based on detected anomalies or alerts. For example, an anomaly detected by Nexus Dashboard can trigger a Splunk alert, which in turn can invoke automated remediation workflows through webhooks, accelerating incident response and reducing manual intervention.
These features and use cases are enabled by the architectural integration of Splunk within Nexus Dashboard, leveraging streaming telemetry to deliver real-time, actionable insights directly at the data source. The Splunk Validated Architecture outlines deployment options and best practices across key areas, including security, application framework, premium apps, and data ingestion, to help organizations fully leverage the capabilities of Splunk Operator for Kubernetes.
Now available to order: Native Splunk 3-node cluster in Cisco Nexus Dashboard #
Cisco Nexus Dashboard now supports ordering a 3-node cluster configuration for native Splunk, designed specifically for production use cases requiring high availability and scalability.
Embedding Splunk natively on Nexus Dashboard with a 3-node cluster enables on-premises analytics without cloud dependency and provides single-console access for analytics, troubleshooting, and audit. It also supports custom dashboards and Splunk search on Nexus Dashboard telemetry.
The 3-node cluster configuration enables customers to deploy native Splunk in a robust, scalable, and production-ready Nexus Dashboard environment, improving data center analytics and operational insights. It provides added resilience by requiring at least two primary nodes to remain operational. This cluster size supports adding nodes for scaling and high availability.
Production readiness
This new orderability option scales to 3-node clusters for production-ready AI and data center networks. But single-node clusters for test environments will continue to be supported.
Deployment and licensing
Native Splunk can be deployed with Nexus Dashboard ND-NODE-G5S and ND-NODE-G5L physical nodes, supporting up to 10 GB/day data ingest with 30-day retention. It is included as an add-on license with the Cisco Data Center Networking (DCN) Premier license. Users launch Splunk directly from Nexus Dashboard’s Analysis Hub, enabling seamless access to embedded analytics.
Ready to transform your data center analytics? #
Native Splunk in Cisco Nexus One represents a convergence of Cisco’s data center networking expertise with Splunk’s powerful analytics capabilities. By embedding Splunk natively on-premises, Cisco empowers organizations to achieve faster troubleshooting, enhanced compliance, and operational efficiency. These are critical capabilities for modern data center fabrics and AI-driven workloads.
It’s time to transform data center operations with real-time, actionable insights and unified analytics. Native Splunk in Cisco Nexus One is a game-changing solution that delivers immediate value out of the box.