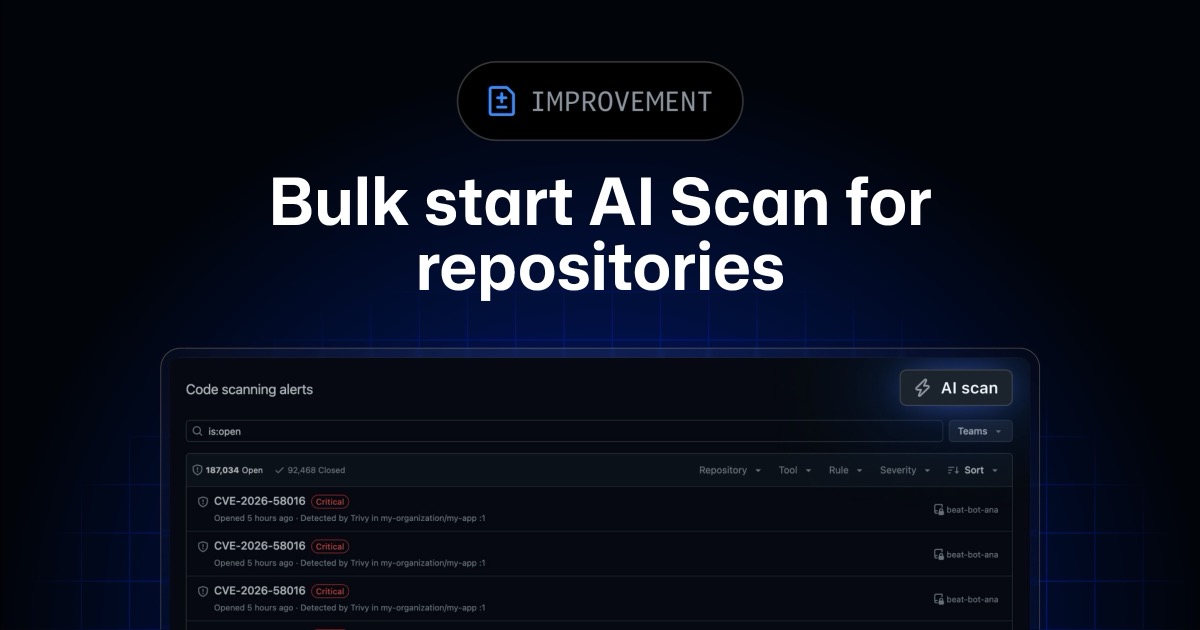
AI Scan for repositories finds security vulnerabilities on your repository’s default branch. It covers languages CodeQL doesn’t support and finds additional issues in languages CodeQL already analyzes. Findings appear in your code scanning backlog alongside CodeQL alerts.
You can now start AI Scans for up to 20 repositories at once. Start scans for selected repositories when you enable the organization-level setting, or from the code scanning organization alerts page. You can also start a scan for an individual repository from its alerts page.
Bulk start for AI Scan for repositories is in public preview. AI Scan for repositories is available on github.com and GitHub Enterprise Cloud with data residency. A GitHub Copilot license isn’t required.
Learn more about AI Scan and join the discussion in GitHub Community.