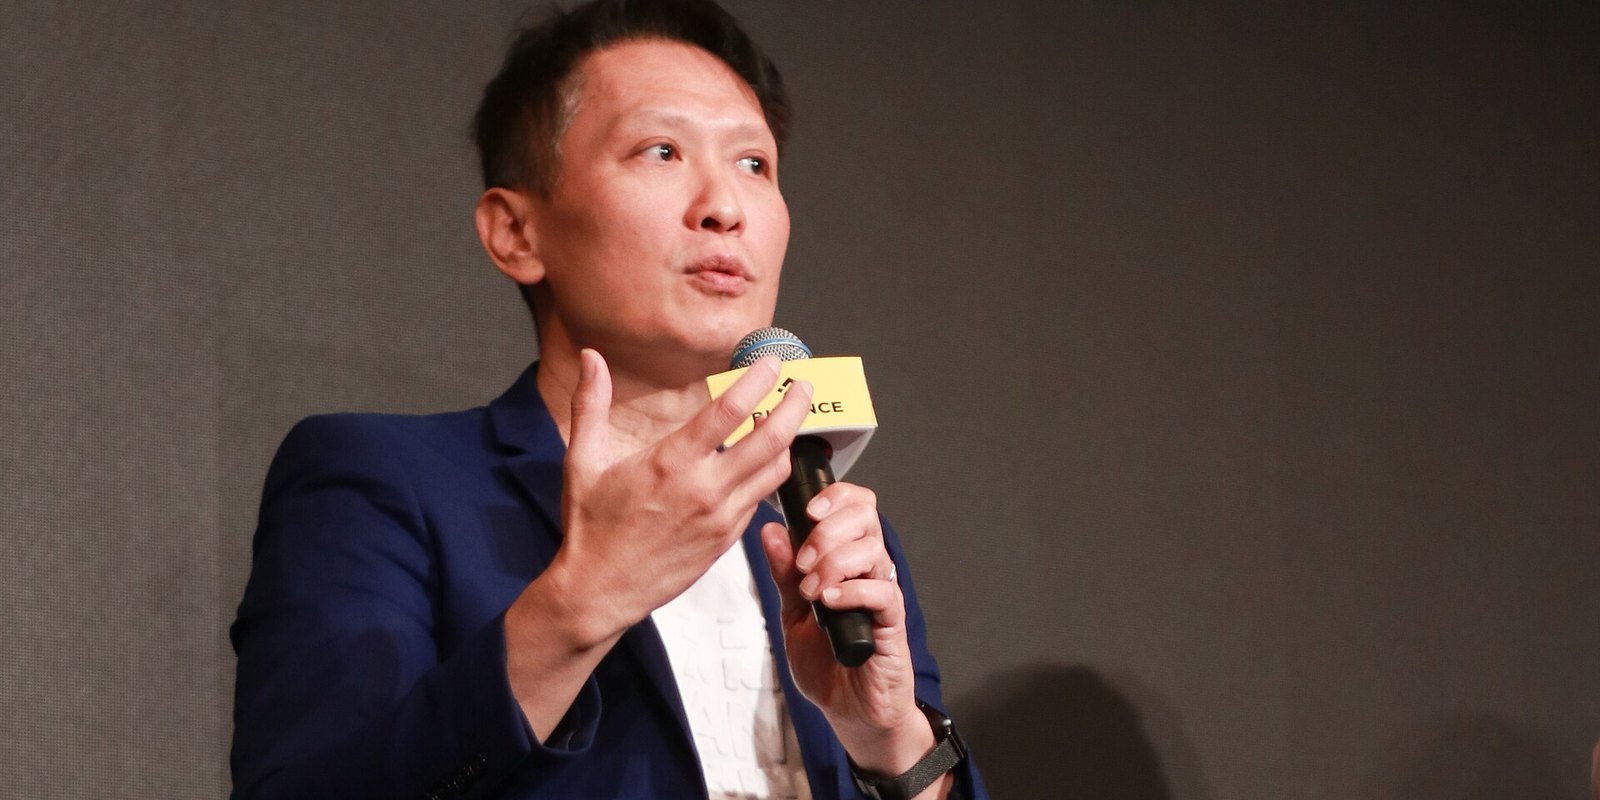
Richard Teng, now Binance’s co-CEO, speaking at Binance Blockchain Week in Istanbul in November 2023, when he was its head of regional markets. Image: Binance / Wikimedia Commons, CC BY 4.0, cropped

The biggest crypto theft on record began with a Binance engineer searching online for an AI coding tool. In its initial incident report, published on Tuesday, Binance says hackers spent four months working their way into its wallet team, then used one of the exchange’s own internal AI tools to take over the computers that let them drain about $6.34bn on October 29.
It is the first detailed account of how the attackers got in. Binance’s report cites the FBI’s finding that North Korea was responsible; Pyongyang has rejected the claim.
A fake installer, then a fake job #
According to Binance, the attack started in June, when an engineer on its Wallet DevOps team downloaded “a tampered Homebrew installation in order to install a popular AI coding tool after searching for it on a search engine”. Binance doesn’t name the AI tool. It replaced the laptop and rotated credentials, but admits the engineer’s role and wallet team colleagues had already been “exposed to the hacker”.
Binance co-CEO Richard Teng described that first step on CNBC on Tuesday:
In June, [the attackers] set up a fake version of a developer tool and lured one of our engineers to install that.
Richard Teng, Binance co-CEO, on CNBC
In September a second engineer, whose profile on a job-hunting platform mentioned Binance, was approached by a fake project director. After a video interview with a supposed HR representative, the second round was with a man claiming to run a company that doesn’t exist. Near the end, the engineer was told to download an “assignment” to his work computer: a malicious code repository that ran during setup. Binance says this zero-day malware swapped a developer tool for a malicious copy and slipped past its endpoint security.
Binance’s own AI tool became the springboard #
The step that turned two infected laptops into a heist came on October 20. Binance says the attacker used the second engineer’s computer “and used an internal AI tool to gain control” over the first wallet engineer and a third, Wallet Software Engineer C. On the first engineer’s computer it found a token that allowed it to deploy containers.
Binance doesn’t say what the tool is, which AI model it runs on or how it was abused, only that it has been rebuilt with new access controls. The report lists “compromised internal AI tooling” alongside fake recruitment interviews, malicious downloads and endpoint compromise as the techniques behind “a sophisticated, multi-stage campaign”, not “a single isolated breach or a simple phishing incident”.
On October 29, between 17:15 and 19:56, the attacker logged on to Engineer C’s computer, used Engineer A’s stolen credentials, deployed a container and ran a script that reached Binance’s internal wallet signing service.
$6.34bn gone in an evening #
From 20:05 UTC, five Binance hot wallets sent 233.46 million XRP to the attacker, followed by SOL, OP and 18,270 BTC. On Ethereum, it used EIP-7702, a feature that lets a wallet hand control to a smart contract, to take over a hot wallet; pausing withdrawals didn’t cancel that permission, and the last transfer landed at 23:56 UTC. Blockchain analytics firm TRM Labs, which traced the outflows, counts about $6.36bn taken across ten blockchains, most of it in about 20 minutes, roughly four times the $1.5bn Bybit hack of February 2025. It blames TraderTraitor, the North Korean unit behind Bybit.
Binance says about $2.85bn has been frozen or intercepted, that it will absorb the loss rather than pass it to users, and that 98% of the affected tokens had been replenished by October 31. It says it blocked 57 other suspected North Korea-linked attacks this year.
‘Spent months building their way in’ #
Teng told CNBC the attackers “spent months building their way in”, and rejected the idea that one employee’s laptop was a single point of failure. Binance has rebuilt the wallet system, replaced devices and expanded “AI-based behavioural anomaly detection”, and is planning a security research fund with “leading AI companies”. Teng said:
We’re also getting an independent expert to review everything that we have done, and we’ll keep strengthening our defenses as the investigation continues.
Richard Teng, Binance co-CEO, on CNBC
The playbook is familiar. Microsoft said last week that North Korea’s hackers now lean on AI at every step, and developer tools are a favourite way in: a tampered Claude Code extension in Cursor’s marketplace tried to backdoor thousands of developers, and the LiteLLM AI gateway was hijacked to steal API keys in October.
Why it matters #
Binance’s account shows AI cutting both ways inside a company. Engineers hunting for the latest AI coding assistant are an easy target for fake installers, and an internal AI tool with broad reach gave attackers a path from one infected laptop to the people who run the wallets. Any company wiring AI tools into its internal systems now has a $6bn example of what happens when they can reach too far.
Sources: Binance, 29 October Binance Security Incident: Initial Findings and Response Update (November 3, 2026); TRM Labs (October 29, 2026); CNBC interview with Richard Teng (November 3, 2026); Reuters on North Korea’s response (November 2, 2026).