Blog November 5, 2026·Product
Pedro Guzmán
Pedro Guzmán
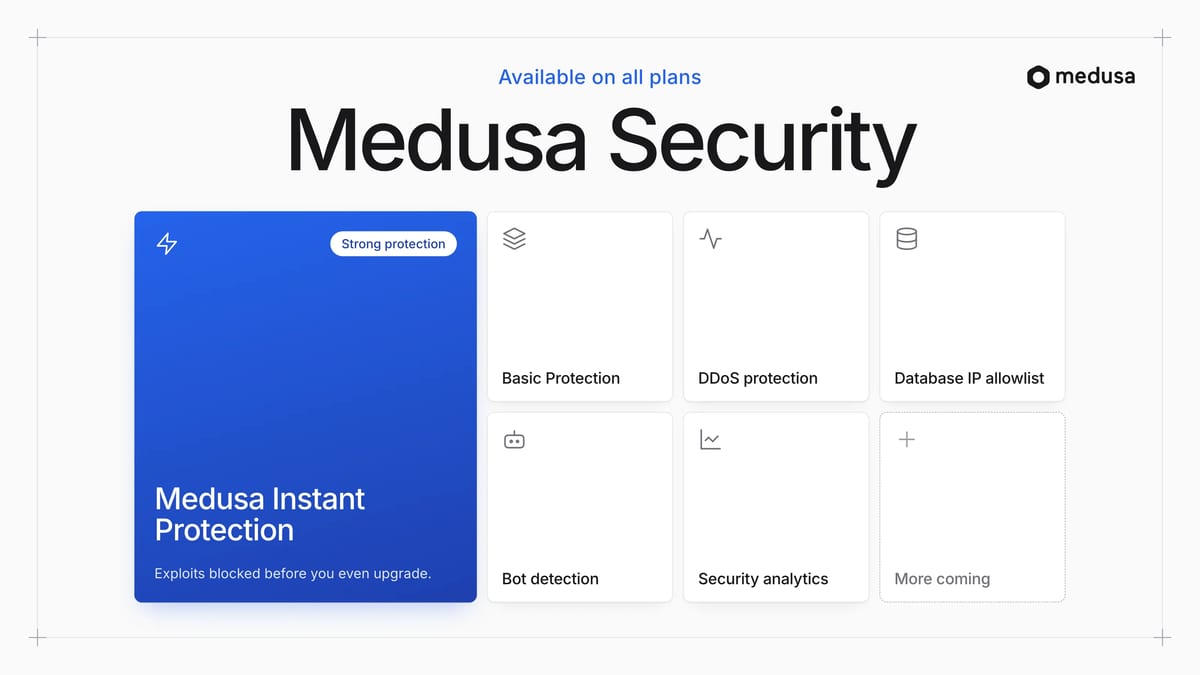
Medusa Security is a new suite of managed security features on Medusa Cloud. It includes Medusa Instant Protection, which blocks exploits against Medusa before you upgrade, plus DDoS protection, bot detection, a database IP allowlist, and more.
Medusa Security is now available on Medusa Cloud. It adds managed security features to the traffic reaching your Medusa applications.
AI agents now analyze and change software faster than ever. That speeds up how quickly vulnerabilities are discovered and increases the volume of automated traffic hitting public applications. Modern JavaScript applications also rely on large dependency graphs that change constantly.
We don't think every team building on Medusa should have to assemble its own security stack. Firewall rules, DDoS mitigation, and bot protection should come with the platform.
What Medusa Security includes #
Medusa Security includes five features:
- Medusa Instant Protection: Blocks requests that try to exploit vulnerabilities and attack patterns common to Medusa applications. E.g. exploitable vulnerabilities in Medusa or NodeJS would be blocked before you've had a chance to upgrade.
- Basic Protection Ruleset: Blocks requests that try to exploit common web attacks and widely exploited vulnerabilities.
- DDoS protection: Detects and mitigates distributed denial-of-service attacks at the network and application levels.
- Bot detection: Blocks requests from malicious bots, while letting verified bots such as search engine crawlers through.
- Database IP allowlist: Restricts public access to your environment's database, or allows access only from the IP addresses you specify.
The first four run at the edge, so malicious requests are stopped before they even reach your application.
Medusa Instant Protection #
Medusa Instant Protection is the most important part of the product.
We build both the commerce framework and the Cloud platform. That lets us turn vulnerabilities identified in Medusa into protections enforced at the edge.
When we discover a new attack vector affecting Medusa, we deploy a mitigation before malicious traffic reaches applications running on Medusa Cloud. Your applications are protected even before you upgrade to a version that fixes the vulnerability. You should still update regularly to get the fix in your codebase.
Analytics #
You can see how rulesets are being applied on your traffic in the Security Analytics page. It helps you understand when and how your application is being attacked, and which rulesets are blocking such attacks. You can see samples of blocked requests with detailed information and you can also search a specific blocked request by ID.
Rollout #
Medusa Security is automatically enabled for all new projects.
For existing projects, only Medusa Instant Protection is automatically enabled. If you want to enable the other protections too, you can do it from the Security settings in your project. We strongly recommend you to do it, so your application security gets hardened right away. If you are worried about it blocking legitimate requests, you can enable it first on a preview or staging environment and see how it performs, and then enable it for production. You can always disable it if you notice too many false positives. In a second phase, a few weeks from now, we will automatically enable all protections for all existing projects, and disabling it won't be possible. We will send a notification to the organization owner before doing so.
More is coming #
This first release focuses on making applications safer by default. Medusa Security will continue to evolve with more advanced features in the coming months. Stay tuned.
Get started #
Medusa Security is available on Medusa Cloud today. Learn how to manage it in the Medusa Security documentation.