cd /news/ai-tools/ai-scan-for-pull-requests-generally-… · home › topics › ai-tools › article
[ARTICLE · art-150746] src=github.blog ↗ pub= topic=ai-tools verified=true sentiment=↑ positive

AI Scan for pull requests generally available

GitHub made AI Scan for pull requests generally available, a code scanning feature that complements CodeQL by finding vulnerabilities in pull request changes for languages and frameworks CodeQL does not currently cover, including PHP, Shell/Bash, Terraform configuration (HCL), Dockerfiles, JSP for Java, and Blazor for C#. AI Scan runs automatically on pull requests when code scanning and the repository's effective AI Scan setting are enabled, and its findings are advisory — they do not fail the code scanning check and cannot block merges through ruleset requirements. AI Scan is available for public repositories owned by organizations or personal accounts, requires GitHub Code Security or GitHub Advanced Security for private and internal organization-owned repositories, and consumes Code Security AI Credits.

by read1 min views1 publishedOct 15, 2026
AI Scan for pull requests generally available
Image: GitHub Changelog

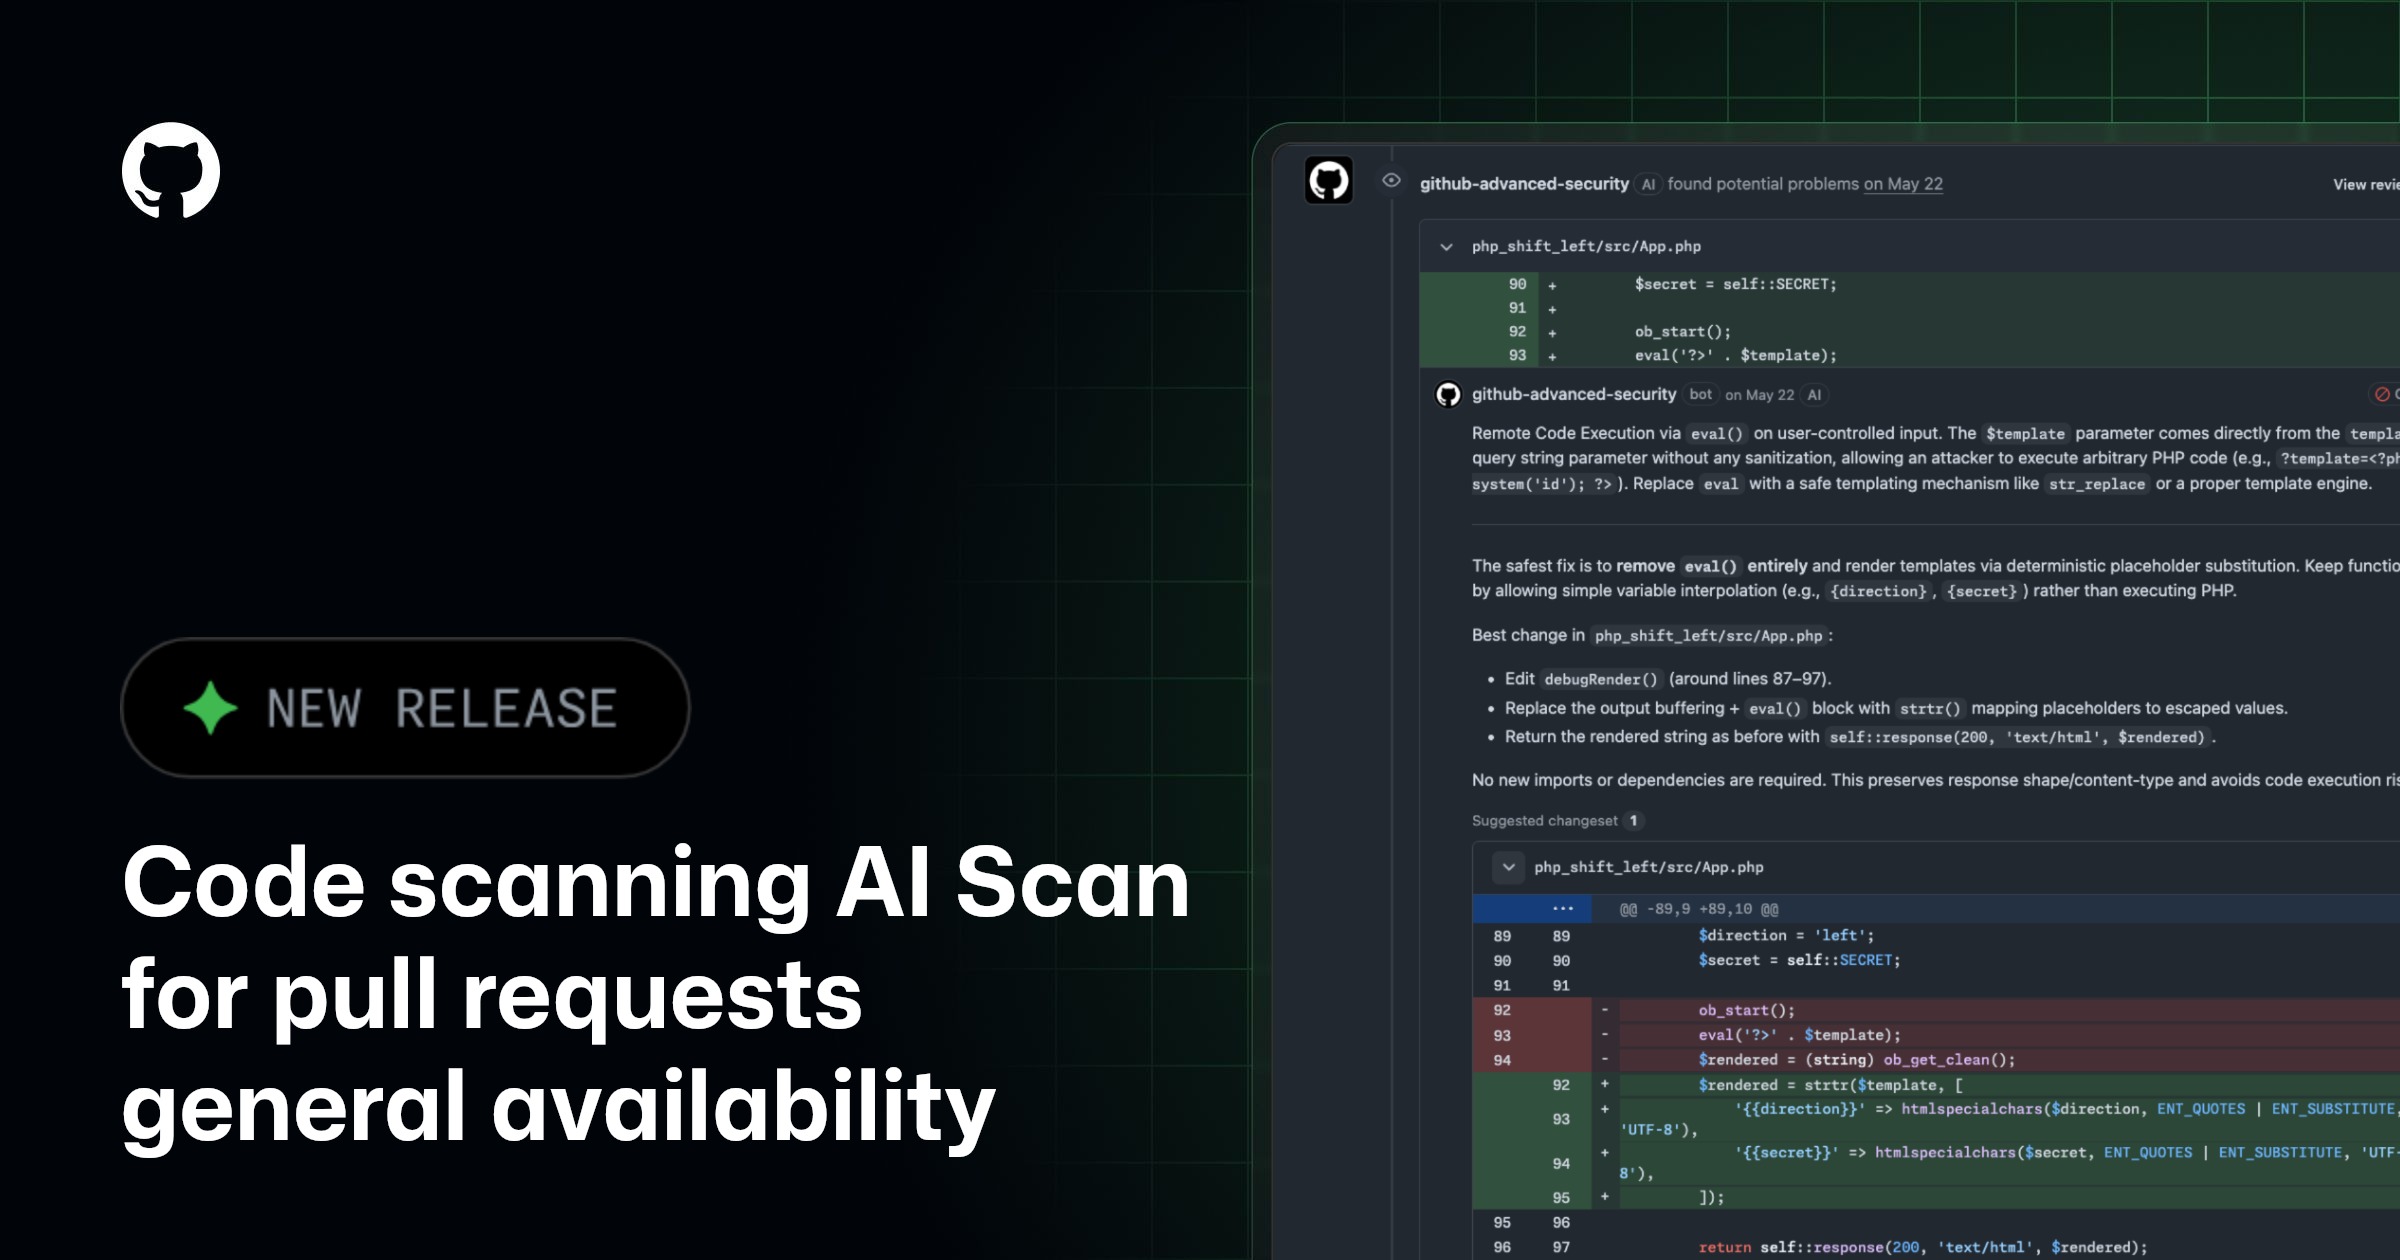
Code scanning AI Scan for pull requests is now generally available. It complements CodeQL by finding vulnerabilities in pull request changes for languages and frameworks that CodeQL does not currently cover, including PHP, Shell/Bash, Terraform configuration (HCL), Dockerfiles, JSP for Java, Blazor for C#, and more.

How it works #

AI Scan runs automatically on pull requests when code scanning and the repository’s effective AI Scan setting are enabled. Findings appear alongside CodeQL results on the Conversation and Files changed tabs, with an “AI” indicator to distinguish them from CodeQL alerts. Findings can include an explanation of the security risk and a suggested autofix.

AI Scan findings are advisory. They do not fail the code scanning check and cannot block pull request merges through ruleset requirements. AI Scan does not run on pull requests from forks or pull requests created by Dependabot.

Availability #

AI Scan is available for public repositories owned by organizations or personal accounts. For private and internal organization-owned repositories, GitHub Code Security or GitHub Advanced Security is required. A GitHub Copilot license is not required.

Billing #

AI Scan for pull requests consumes Code Security AI Credits. AI Credit usage is displayed in the “AI usage” section of enterprise billing and licensing as the “Advanced Security” product. You can also set SKU-level budgets for Code Security AI Credits. Learn more about usage-based billing.

Learn more about AI Scan for pull requests and billing for GitHub Advanced Security AI features.

Join the discussion in the AI Scan Community discussion.

── more in #ai-tools 4 stories · sorted by recency
── more on @github 3 stories trending now
sponsored brought to you by zahid.host 4,200+ EU-deployed projects
reading about agents? ship yours in a single git push.

Run your AI side-project on zahid.host

EU-based hosting, git-push deploys, automatic HTTPS, no cold starts. Free tier with a custom domain — perfect for shipping the agent you just read about.

$git push zahid main
→ Live at https://your-agent.zahid.host ✓
Get free account → Pricing
from €0/mo · no card required
LIVE [news/ai-scan-for-pull-req…] indexed:0 read:1min 2026-10-15 · —